Ravie LakshmananSep 01, 2026Vulnerability / Supply Chain Attack Threat actors are exploiting a newly patched critical security flaw impacting JFrog Artifactory merely days after public disclosure, according to… Continue reading


Ravie LakshmananSep 01, 2026Vulnerability / Supply Chain Attack Threat actors are exploiting a newly patched critical security flaw impacting JFrog Artifactory merely days after public disclosure, according to… Continue reading
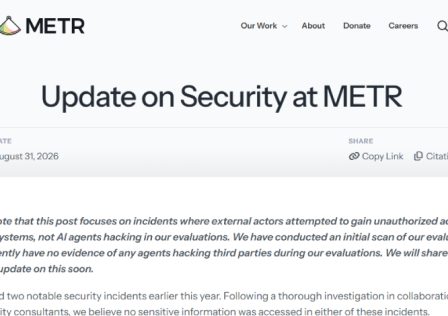
Ravie LakshmananSep 01, 2026Cyber Attack / Artificial Intelligence METR (short for Model Evaluation and Threat Research and pronounced “Meter”), a research non-profit that evaluates frontier artificial intelligence (AI)… Continue reading
Ravie LakshmananSep 01, 2026Vulnerability / Artificial Intelligence Threat actors are exploiting two critical flaws impacting Langflow and Ruby on Rails, according to new findings from VulnCheck. The vulnerabilities… Continue reading
VulnCheck has disclosed two previously undocumented factory implants in firmware for routers built by Shenzhen Zhibotong Electronics (ZBT), each of which gives an unauthenticated remote attacker the ability… Continue reading

Swati KhandelwalAug 28, 2026Vulnerability / Cloud Security ServiceNow has released patches for four security flaws impacting the ServiceNow AI Platform, three of them rated 10.0 on the CVSS… Continue reading
Ravie LakshmananAug 28, 2026Vulnerability / Web Security Malicious actors are exploiting a newly patched security flaw in PaperCut NG and MF to execute arbitrary code on susceptible instances,… Continue reading
The CERT Coordination Center (CERT/CC) has disclosed two unpatched vulnerabilities in Kaltura’s HTML5 video player library that allow a remote, unauthenticated attacker to read arbitrary files from a… Continue reading

Ravie LakshmananAug 25, 2026Vulnerability / Web Security Bad actors are attempting to exploit two severe unauthenticated authentication bypasses in the Xecurify miniOrange SAML 2.0 Single Sign On plugin… Continue reading

Ravie LakshmananAug 25, 2026Vulnerability / Enterprise Security The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a maximum-severity security flaw impacting Oracle HTTP Server and Oracle… Continue reading
Swati KhandelwalAug 24, 2026Vulnerability / Identity Security Red Hat and the Keycloak project have released patches to address a critical security flaw in the open-source identity and access… Continue reading

Copyright 2015 NuclearCoffee Inc. - All Rights Reserved.
Back to Top