The crooks have trust problems of their own. One ransomware affiliate decided to keep the profits for himself. Elsewhere, an attacker left a server exposed, complete with tools… Continue reading
The crooks have trust problems of their own. One ransomware affiliate decided to keep the profits for himself. Elsewhere, an attacker left a server exposed, complete with tools… Continue reading
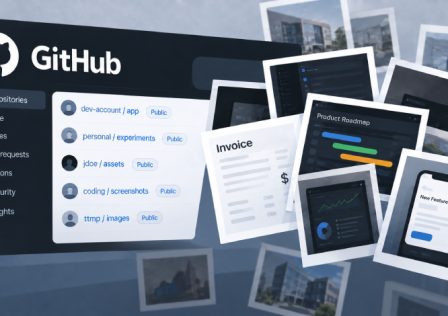
AI coding agents asked to share screenshots of code changes for review have put internal company images in public GitHub repositories, security company Glow said. Its researchers found… Continue reading

Ravie LakshmananSep 15, 2026Vulnerability / Cloud Security Cybersecurity researchers have disclosed details of a mass-scanning campaign that has targeted Vite deployments siphon sensitive data. The first is an… Continue reading

Nearly one in ten of the internet-facing LiteLLM servers that Wiz Research scanned in February accepted sk-1234, the example admin key in LiteLLM’s own setup guide. LiteLLM is an open-source AI… Continue reading

The Hacker NewsSep 09, 2026Security Operations / Artificial Intelligenc A major vulnerability is disclosed. The alert lands immediately. Then comes the harder question: Are we actually exposed? For… Continue reading

Ravie LakshmananSep 05, 2026Data Breach / Vulnerability Hardware wallet manufacturer Trezor on Friday disclosed that another 67,000 customers from the U.S. have been impacted in a breach at… Continue reading

Thomson Reuters disclosed on Wednesday that an unauthorized party obtained files from C-Track, the court case management platform sold by its West Publishing Corporation unit, in March 2026,… Continue reading

Grand Theft Auto VI leakers may be exposed after Rockstar Games filed requests with a federal court for subpoenas. The alleged GTA 6 gameplay leaks were distributed online…. Continue reading

SafePal has disclosed that an authorization flaw in an order-tracking plug-in exposed the names, email addresses, shipping addresses, phone numbers, and purchase details of approximately 39,798 customers. The… Continue reading

Two malicious LiteLLM releases sat on PyPI for about 40 minutes in March carrying credential-stealing code capable of harvesting cloud keys, SSH keys, Kubernetes tokens, database passwords, and… Continue reading
Copyright 2015 NuclearCoffee Inc. - All Rights Reserved.
Back to Top