Two malicious LiteLLM releases sat on PyPI for about 40 minutes in March carrying credential-stealing code capable of harvesting cloud keys, SSH keys, Kubernetes tokens, database passwords, and… Continue reading

Two malicious LiteLLM releases sat on PyPI for about 40 minutes in March carrying credential-stealing code capable of harvesting cloud keys, SSH keys, Kubernetes tokens, database passwords, and… Continue reading
A malicious SIM card can order the device it sits in to run commands of the attacker’s choosing. On the cellular modules built into electric-vehicle chargers, industrial routers,… Continue reading

A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware targeting Windows, Mac,… Continue reading

Two security flaws in Paperclip could let attackers execute commands on a network server or a developer’s computer. Paperclip is an open-source control plane for teams of artificial… Continue reading
A cluster of 77 extensions on the Open VSX marketplace has been found to impersonate legitimate developer tools while transmitting information about the systems and development environments on… Continue reading

Swati KhandelwalAug 04, 2026AI Security / DevSecOps Google deleted three AI agent workflows from its Agent Development Kit (ADK) Python repository. Pillar Security showed that a public GitHub… Continue reading

Cybersecurity researchers have discovered a new set of malicious npm packages that target users of Alibaba developer tools with a cross-platform remote access trojan (RAT) as part of… Continue reading
Swati KhandelwalJul 29, 2026Vulnerability / Browser Security Nebula Security says a patched Firefox JIT flaw could be triggered by simply visiting a malicious webpage and was also used… Continue reading
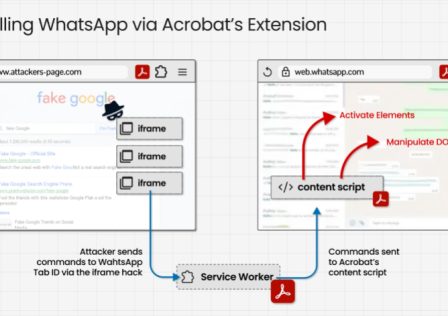
Ravie LakshmananJul 22, 2026Vulnerability / Browser Security Cybersecurity researchers have disclosed details of a now-patched vulnerability chain in the Adobe Acrobat Chrome extension that has over 314 million… Continue reading

Cybersecurity researchers have flagged a new software supply chain attack codenamed SleeperGem targeting the Ruby ecosystem after three malicious gems were published to RubyGems with the end goal… Continue reading
Copyright 2015 NuclearCoffee Inc. - All Rights Reserved.
Back to Top