Cybersecurity researchers have disclosed details of what has been described as a “highly sophisticated infection chain” targeting government organizations in Asia. The activity, detailed by Kaspersky this week,… Continue reading
Cybersecurity researchers have disclosed details of what has been described as a “highly sophisticated infection chain” targeting government organizations in Asia. The activity, detailed by Kaspersky this week,… Continue reading
The North Korea-linked Lazarus Group has been attributed to a cyber espionage campaign dubbed Operation FlashHole targeting at least three organizations in South Korea spanning the construction, software,… Continue reading
Hackers exploited a critical Cisco Catalyst SD-WAN flaw, fixed in February, to plant custom malware inside the systems that control an organization’s SD-WAN network. The malware, called KeyDrift,… Continue reading

A criminal using the Amadey malware can no longer access or steal data from 180,000 infected computers around the world, including some in Australia, the Australian Signals Directorate… Continue reading
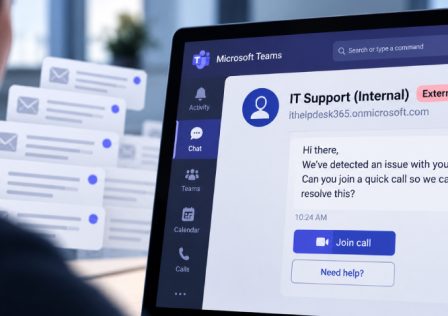
Cybersecurity researchers are calling attention to what they say is a “recurring social engineering pattern” across hundreds of cases in which threat actors use Microsoft Teams’ external chat… Continue reading
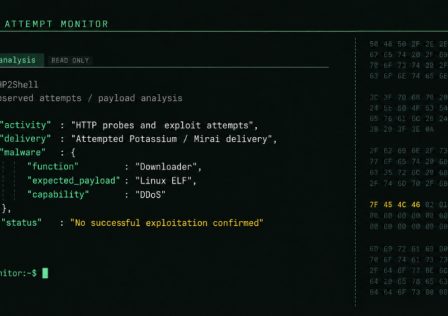
Threat actors have been observed unsuccessfully attempting to exploit the newly disclosed PHP2Shell vulnerabilities to rope infected systems into a Mirai botnet variant called Potassium, as it emerges… Continue reading
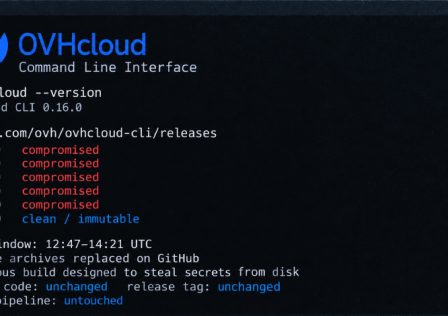
An attacker used a contributor’s GitHub account to replace the download archives on five existing releases of OVHcloud’s command-line tool on Monday, October 19. The account had been… Continue reading
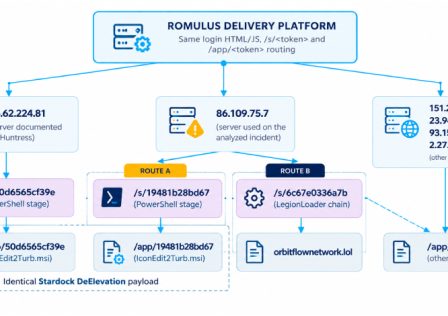
Cybersecurity researchers have disclosed details of a ClickFix delivery platform called ROMULUS that’s being used to distribute malware such as Legion Loader. According to Forescout Research – Vedere… Continue reading
A fake Web3 accelerator has been observed pushing information stealers and backdoors to Windows and macOS systems using malicious npm packages under the pretext of offering free artificial… Continue reading
A suspected advanced threat actor has been observed exploiting a security flaw in Fortinet FortiOS to deliver a previously unreported memory-resident ARM64 malware known as PEERSTITCH. The attack… Continue reading

Copyright 2015 NuclearCoffee Inc. - All Rights Reserved.
Back to Top