Attackers are exploiting a zero-day SQL injection flaw in Arista’s VeloCloud Orchestrator (VCO), the central management system for VeloCloud SD-WAN networks, the company said in an advisory on October 22. The flaw… Continue reading
Attackers are exploiting a zero-day SQL injection flaw in Arista’s VeloCloud Orchestrator (VCO), the central management system for VeloCloud SD-WAN networks, the company said in an advisory on October 22. The flaw… Continue reading
Ravie LakshmananSep 25, 2026Vulnerability / Email Security The Canadian Centre for Cyber Security has warned that a now-patched Roundcube Webmail vulnerability is being actively exploited in the wild…. Continue reading

Swati KhandelwalAug 28, 2026Vulnerability / Cloud Security ServiceNow has released patches for four security flaws impacting the ServiceNow AI Platform, three of them rated 10.0 on the CVSS… Continue reading
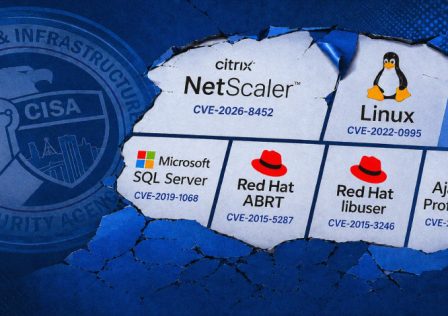
Ravie LakshmananAug 27, 2026Vulnerability / Web Security The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added six flaws to its Known Exploited Vulnerabilities (KEV) catalog, including… Continue reading

Swati KhandelwalAug 06, 2026Database Security / Endpoint Security Attackers broke into an organization’s Oracle database through a SQL injection flaw in a public-facing web application, then installed a… Continue reading

Swati KhandelwalAug 04, 2026Vulnerability / Database Security cPanel has patched a flaw that let an authenticated hosting customer execute SQL in the database’s root context, crossing the privilege… Continue reading
Copyright 2015 NuclearCoffee Inc. - All Rights Reserved.
Back to Top