Google on Tuesday said it’s rolling out improved safeguards in its Chrome browser to secure users against ClickFix attacks when Enhanced Protection is enabled. ClickFix is a popular… Continue reading
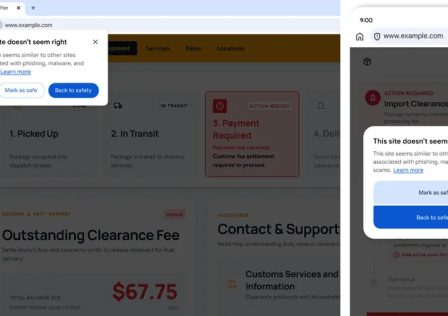
Google on Tuesday said it’s rolling out improved safeguards in its Chrome browser to secure users against ClickFix attacks when Enhanced Protection is enabled. ClickFix is a popular… Continue reading
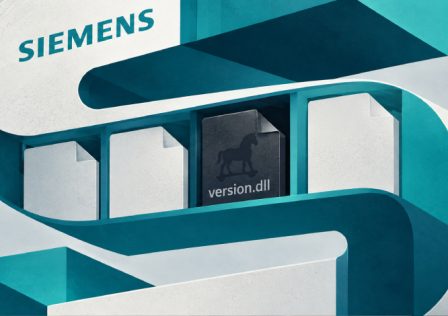
Siemens has addressed a DLL sideloading vulnerability impacting Siemens Software Center that it said has been exploited in ClickFix attacks. The high-severity vulnerability, tracked as CVE-2026-110936 (CVSS v4… Continue reading
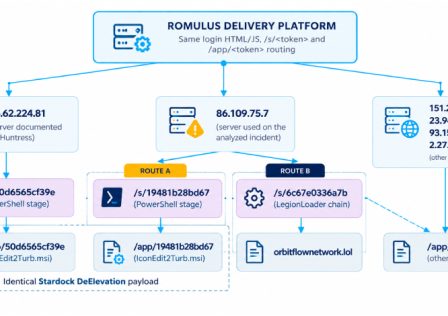
Cybersecurity researchers have disclosed details of a ClickFix delivery platform called ROMULUS that’s being used to distribute malware such as Legion Loader. According to Forescout Research – Vedere… Continue reading

A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser’s cache. “Instead of downloading and… Continue reading
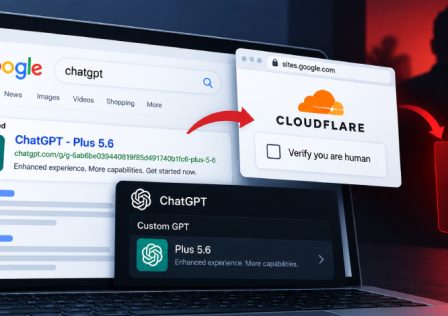
Ravie LakshmananSep 30, 2026Malware / Artificial Intelligence Threat actors are abusing ChatGPT Custom GPTs to disguise them as legitimate product offerings and direct unsuspecting victims to malicious sites… Continue reading

ClickFix has become the most common way attackers get into enterprise networks, and it does it without an exploit, an attachment, or a file on disk. Our new… Continue reading

An active ClickFix campaign has been observed compromising legitimate Ukrainian business websites to inject bogus Cloudflare verification pages and trick victims into downloading a previously undocumented information stealer… Continue reading

A browser. A plugin. A package. A login screen. Normal stuff. That is basically the problem this week. The trouble keeps showing up inside things people already trust:… Continue reading

Threat actors are leveraging ClickFix-like lures to deliver a previously undocumented remote access trojan (RAT) called ChainScript. “ChainScript has appeared under multiple build names, including ComponentTask33, UpdateDigital, HostShared,… Continue reading
Cybersecurity researchers have flagged two new malware families called WordlistLoader and SynkLoader that’s used to deliver next-stage payloads and likely sell access to ransomware groups. According to findings… Continue reading
Copyright 2015 NuclearCoffee Inc. - All Rights Reserved.
Back to Top