Ravie LakshmananAug 07, 2026Malware / Social Engineering ClickFix-style attacks are being used to deliver a Go-based malware capable of stealing cryptocurrency assets, as well as browser-stored passwords, Apple… Continue reading
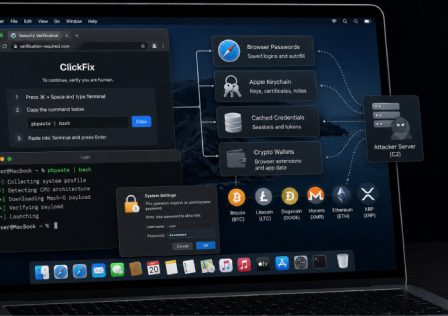
Ravie LakshmananAug 07, 2026Malware / Social Engineering ClickFix-style attacks are being used to deliver a Go-based malware capable of stealing cryptocurrency assets, as well as browser-stored passwords, Apple… Continue reading
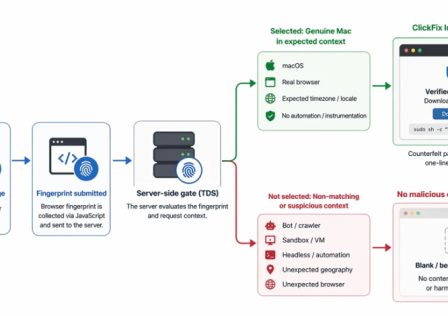
A macOS ClickFix operation spanning more than 250 front-end domains now fingerprints visitors before deciding whether to show them a malware lure, a change Microsoft Threat Intelligence tracked… Continue reading
A new Russian loader-as-a-service (LaaS) codenamed DOUBLECUP has been using ClickFix lures as a way to stage malware-laced PNG images in victims’ browser cache and ultimately deliver CountLoader… Continue reading

Ravie LakshmananJul 27, 2026Cybersecurity / Hacking Monday starts with the usual promise that everything is under control. Then the logs wake up. This week, trusted tools crossed lines,… Continue reading
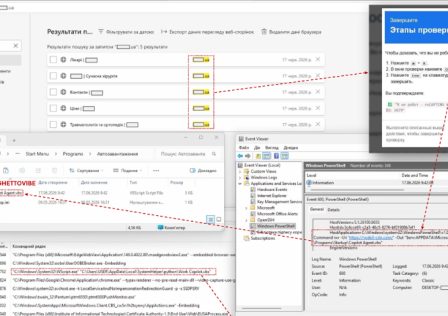
Ravie LakshmananJul 19, 2026Malware / Cyber Warfare Russian state-sponsored threat actors have been observed leveraging the infamous ClickFix strategy to trick Ukrainian targets into infecting their own machines… Continue reading

ACR Stealer, an infostealer in circulation since 2024, is walking out of enterprise networks with saved browser passwords, live session tokens, PDFs, Microsoft 365 documents, and files from… Continue reading
Cybersecurity researchers have called attention to a new modular malware called TELEPUZ that’s been spreading via websites infected with ClickFix lures since late April 2026. “The malware is… Continue reading
Copyright 2015 NuclearCoffee Inc. - All Rights Reserved.
Back to Top