Ravie LakshmananSep 30, 2026Malware / Artificial Intelligence Threat actors are abusing ChatGPT Custom GPTs to disguise them as legitimate product offerings and direct unsuspecting victims to malicious sites… Continue reading
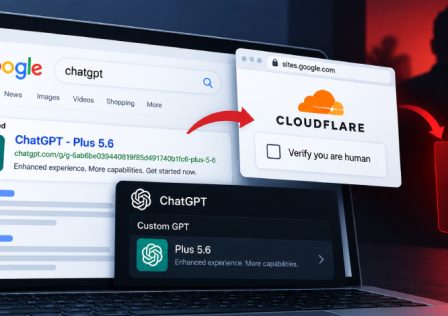

Ravie LakshmananSep 30, 2026Malware / Artificial Intelligence Threat actors are abusing ChatGPT Custom GPTs to disguise them as legitimate product offerings and direct unsuspecting victims to malicious sites… Continue reading

An active ClickFix campaign has been observed compromising legitimate Ukrainian business websites to inject bogus Cloudflare verification pages and trick victims into downloading a previously undocumented information stealer… Continue reading

Threat actors are leveraging ClickFix-like lures to deliver a previously undocumented remote access trojan (RAT) called ChainScript. “ChainScript has appeared under multiple build names, including ComponentTask33, UpdateDigital, HostShared,… Continue reading
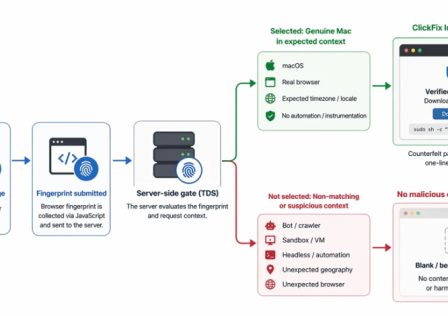
A macOS ClickFix operation spanning more than 250 front-end domains now fingerprints visitors before deciding whether to show them a malware lure, a change Microsoft Threat Intelligence tracked… Continue reading

Ravie LakshmananJul 27, 2026Cybersecurity / Hacking Monday starts with the usual promise that everything is under control. Then the logs wake up. This week, trusted tools crossed lines,… Continue reading

ACR Stealer, an infostealer in circulation since 2024, is walking out of enterprise networks with saved browser passwords, live session tokens, PDFs, Microsoft 365 documents, and files from… Continue reading

A new banking fraudulent operation is targeting customers of Mexican banks, fintech, payment processors, and cryptocurrency exchanges using ClickFix lures. The activity cluster, tracked by Elastic Security Labs… Continue reading

A Brazilian banking trojan called Ousaban is going after Windows users who bank in Spain and Portugal. Fortinet’s FortiGuard Labs identified the campaign in May 2026. It opens with a… Continue reading
Copyright 2015 NuclearCoffee Inc. - All Rights Reserved.
Back to Top