GitHub has announced that it’s introducing a new package firewall as a preview to block installation of suspicious npm packages during installation time. “The firewall inspects both metadata… Continue reading
GitHub has announced that it’s introducing a new package firewall as a preview to block installation of suspicious npm packages during installation time. “The firewall inspects both metadata… Continue reading
A fake Web3 accelerator has been observed pushing information stealers and backdoors to Windows and macOS systems using malicious npm packages under the pretext of offering free artificial… Continue reading
Cybersecurity researchers have discovered a malicious npm package that’s part of a recently disclosed software supply chain attack campaign dubbed MALFEX. The package, named “imgdecode,” was uploaded to… Continue reading
GitHub has taken the step of expiring unvalidated npm trusted publishing configurations 48 hours after creation after researchers found that it was possible for an attacker to push… Continue reading

The npm package known as “tensorlake,” a TypeScript software development kit (SDK) for Tensorlake applications, sandboxes, and cloud services, was compromised as part of a ChainDrop / Shai-Hulud… Continue reading
Ravie LakshmananOct 07, 2026Supply Chain / Malware Cybersecurity researchers have disclosed details of a long-running npm supply chain malware campaign that pushes information stealers and remote access trojans… Continue reading
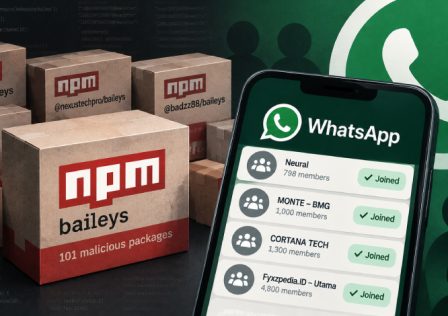
Ravie LakshmananSep 29, 2026Supply Chain / Malware Cybersecurity researchers have identified a cluster of 101 npm packages that are used to trap developers into a WhatsApp group subscriber… Continue reading

A malicious npm package named “indexed-btree” has been observed hiding its malicious behavior within application code rather than using lifecycle scripts, indicating that threat actors are likely shifting… Continue reading

Ravie LakshmananSep 23, 2026Malware / Cloud Security Unknown threat actors have managed to compromise two legitimate MemTensor packages across the npm and Python Package Index (PyPI) repositories to… Continue reading
Ravie LakshmananSep 22, 2026Supply Chain Attack / Malware Cybersecurity researchers have disclosed details of a malicious npm package named “tw-pkgprobe-7731” that masquerades as a security tool targeting developers… Continue reading

Copyright 2015 NuclearCoffee Inc. - All Rights Reserved.
Back to Top